Watch everything.
Secrets get pasted into AI coding assistants every day, and the session logs keep them on disk, unencrypted.
Skarn reads the session logs your AI coding assistants already write, and surfaces the leaked credentials and the attacks that exploit them. It runs entirely on the local machine - no upload, no network call by default, nothing leaves it.
Skarn is the local-first, no-egress forensic layer for the AI-session surface the inline and cloud tools disclaim: local-disk session content, MCP and tool-call detail, and post-hoc attack-chain reconstruction with a session risk score.
Nothing leaves the machine. The free tier is the full local scanner; Pro adds the paid controls and Team the organization around them. Built for regulated, audit-heavy, EU data-residency environments.
Not an engineer? Find your view.
What matters to you is not what matters to them. See what Skarn means for your role - the business risk, the security posture, the compliance position, or the developer view.
Every session is written to disk.
Every AI coding assistant - Claude Code, Gemini CLI, Antigravity, Codex CLI, Cursor, GitHub Copilot, Kimi Code CLI, Grok Build, Grok Bot, OpenCode, Cline, Cowork, Claude Enterprise - writes the whole conversation to disk: every prompt, every file it read, every command it ran, unencrypted. Developers paste keys, passwords, and .env files into those sessions all day long, and commits co-authored by Claude Code leaked secrets at roughly twice the rate of all public GitHub commits (3.2% vs 1.5%, GitGuardian State of Secrets Sprawl 2026). A secret scanner pointed at a git repository never reads these logs, and a measured teardown of what those logs contain shows why that matters.
What you can answer today, and after one scan
| The question | With the assistants as installed | After skarn assess on the same machine |
|---|---|---|
| Which credentials went into an AI coding session? | Each assistant keeps its own session store on the developer's disk, in its own format and location. The vendor documentation we reviewed for Claude Code, Codex, Cursor, Copilot and Gemini describes transcripts, audit logs and usage metrics, and no report of the credentials inside sessions. Repository secret scanners read repositories. | One list over every supported assistant on the machine: each credential masked, with its severity and what kind of credential it is. The HTML report adds the rule and the session for each. |
| Was a session steered into reading a secret and sending it somewhere? | The steps are separate tool calls inside one transcript, or across several. Finding them means reading transcripts by hand. | The read, the injection and the outbound call are linked into one attack chain. It raises the machine's risk score, and the HTML report maps each finding in it to MITRE ATLAS. |
| Can security see a finding without seeing the secret? | The session files these assistants write hold the secret in full. | A redacted Markdown or HTML report, or a dossier scoped to one finding. No report carries a secret in full. |
| How exposed is this machine, as a number? | The assistants report none. | A risk score from 0 to 100 with its band, and severity counts. |
| How far back does it go? | As far as each assistant keeps its sessions. Claude Code and Gemini CLI delete sessions older than 30 days by default. | The same. Skarn reads what is on disk and changes none of it. |
skarn assess needs no account and no license, and the scan makes no network call. Install Skarn and run it, or open a sample report first.
What leaked, made visible.
Run Skarn on a machine and it reads the AI session logs already on disk, across every assistant, and shows the live credentials and the attacks around them. Redacted, scored, and attributed to the exact session. In minutes, on the machine, nothing uploaded.
Every credential, masked
251 detection rules - 155 community secret patterns plus 96 AI-specific - pulled straight out of past AI sessions: AWS keys, database URIs, and every major AI provider key (OpenAI, Anthropic, Bedrock, Cursor, and 30+ more), each shown masked, at a measured false-positive rate.
The attack around the key
The prompt-injection-to-exfiltration attack chain an ordinary secret scanner can't see: poisoned content driving a read, then a leak.
A risk score you can act on
One number per session and per team for a dashboard or a CI gate, so exposure becomes a number you measure and drive down.
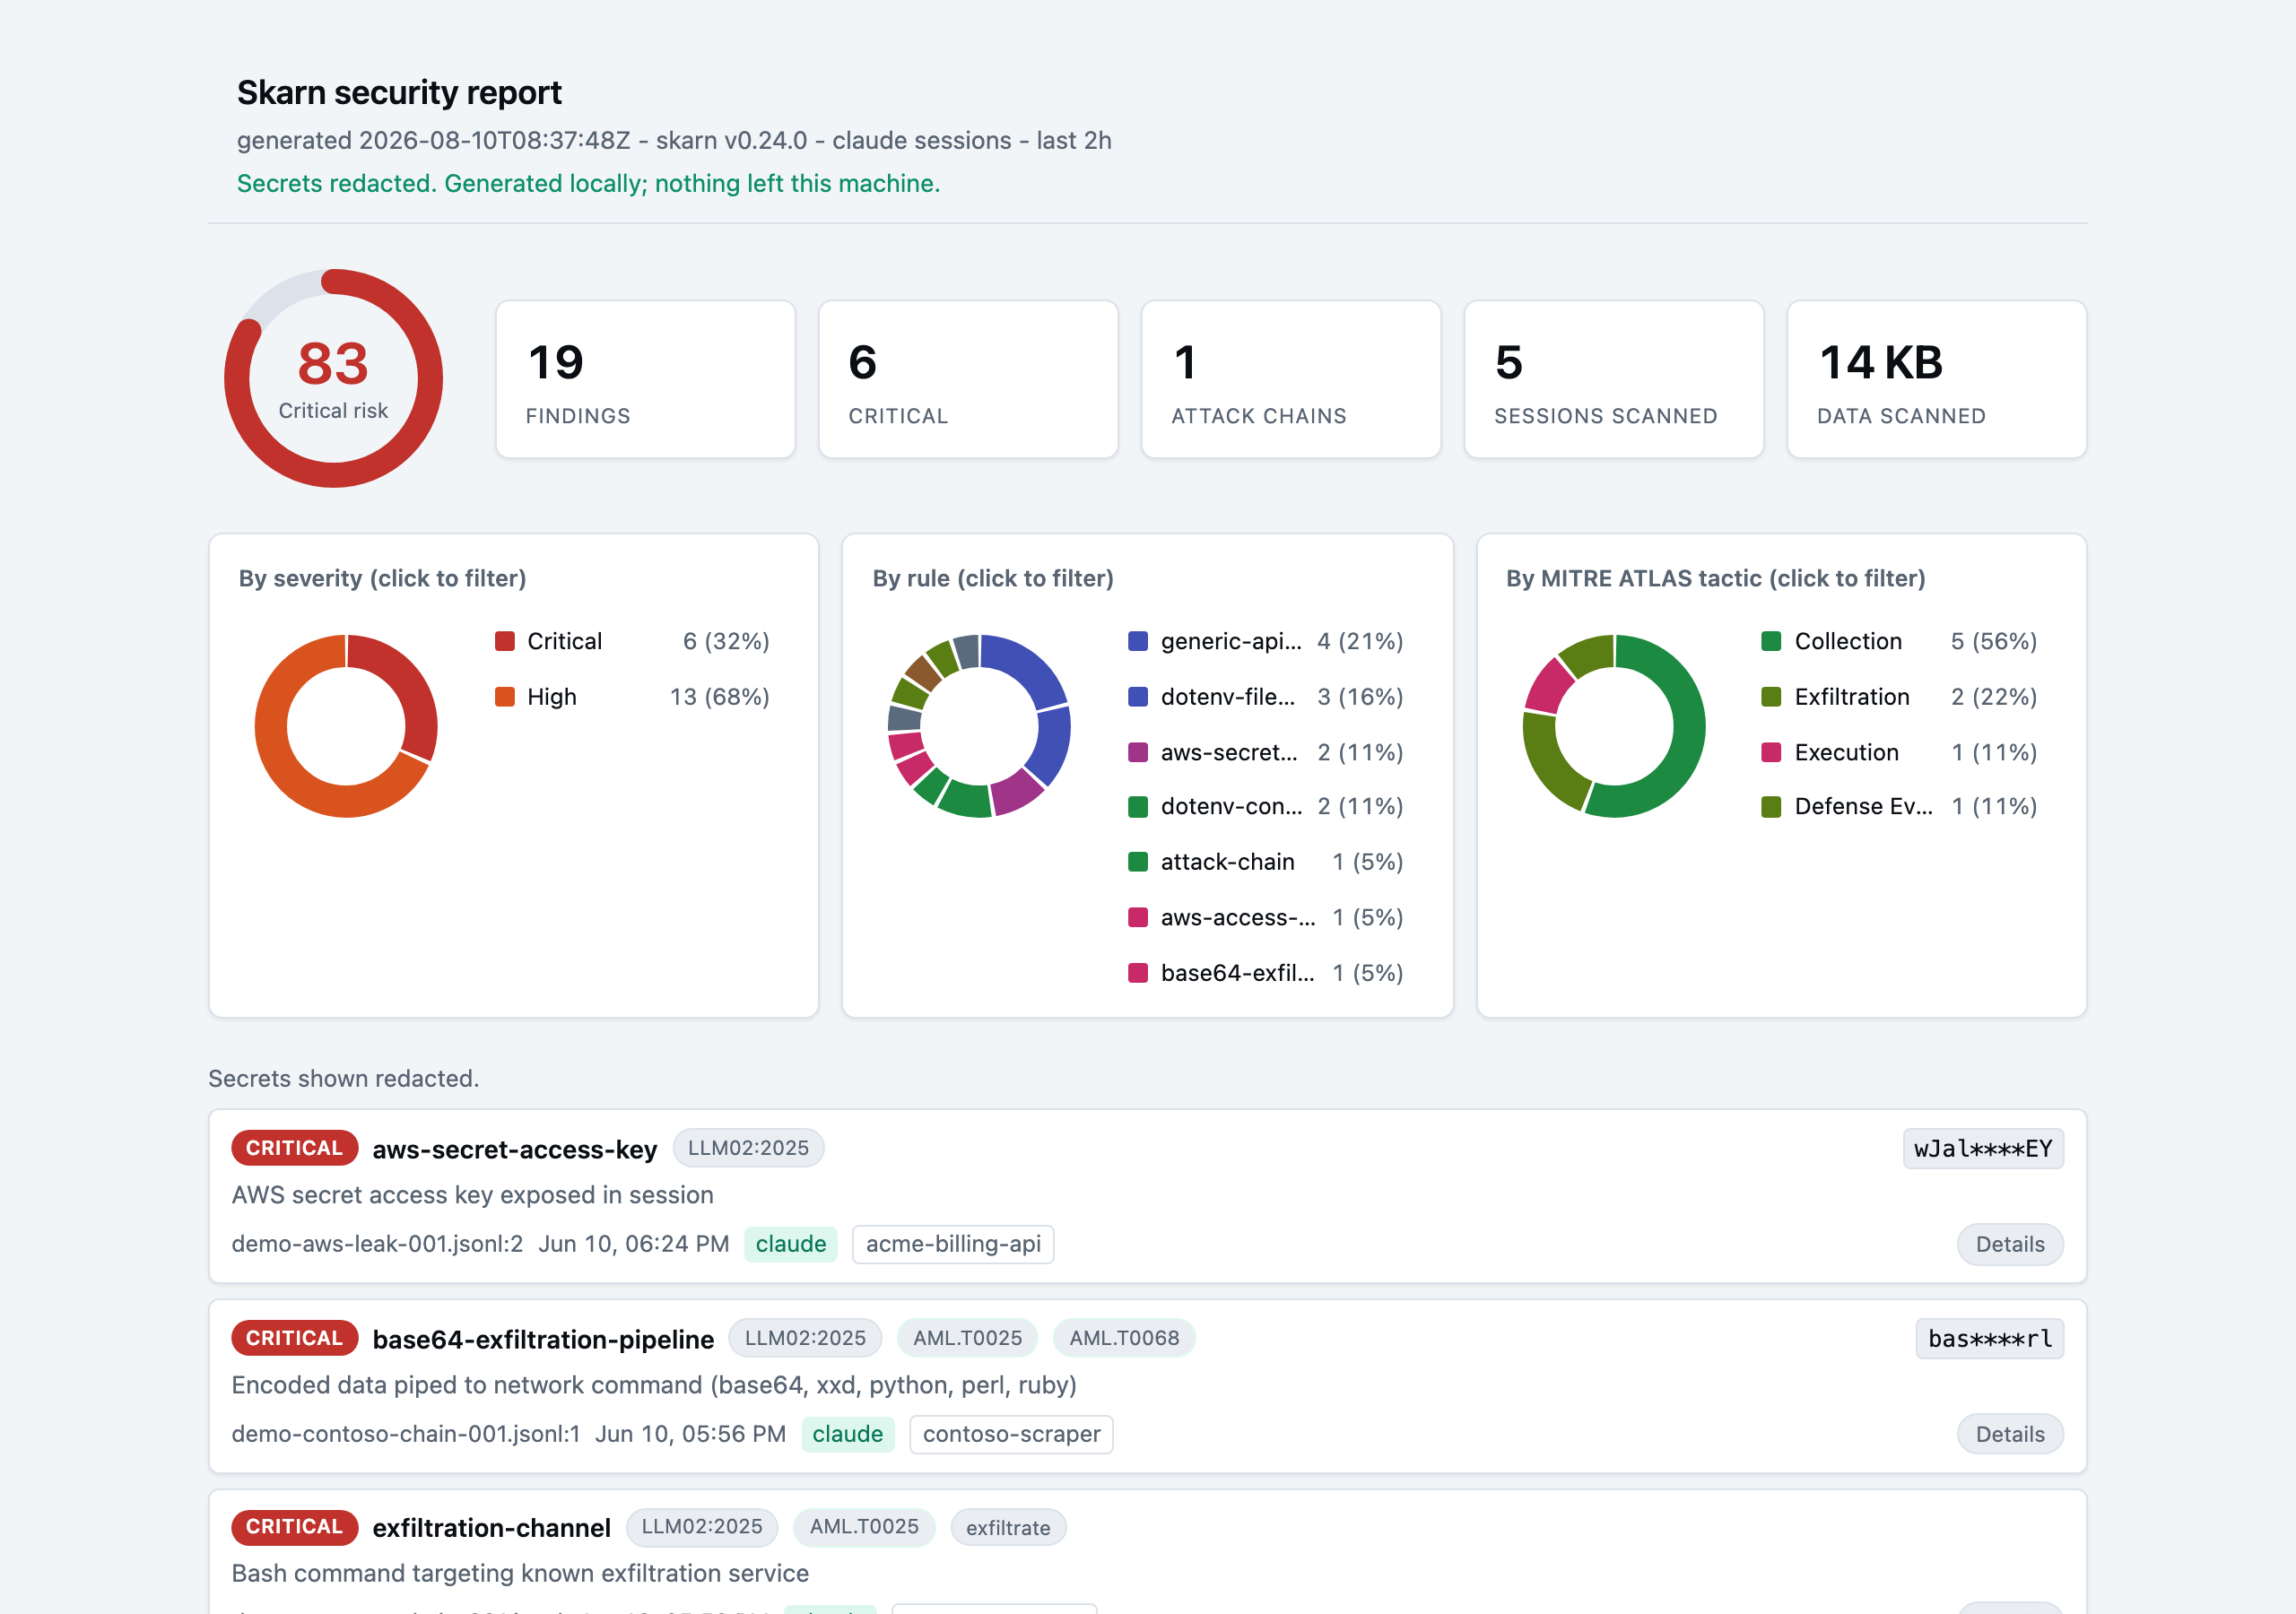
Assess one machine first.
skarn assess scans every AI coding session on a machine and prints a redacted risk summary: a risk score, severity counts, the top exposures, and the top attack chain. It needs no account, no license, and no configuration, and the scan makes no network call. Add -o report.html to keep the full report.
With nothing installed
Why Skarn is different.
Reads the AI sessions
A surface your git secret scanners never look at. The key pasted into a chat and never committed is invisible to them and obvious to Skarn.
Reconstructs the attack
Credential read, prompt injection, and exfiltration, linked into an attack chain correlated across MITRE ATLAS tactic-aligned stages.
Runs on the machine
No upload, no network call by default, no telemetry. The session logs stay on the machine.
One binary, every assistant
Claude Code, Gemini CLI, Antigravity, Codex CLI, Cursor, GitHub Copilot, Kimi Code CLI, Grok Build, Grok Bot, OpenCode, Cline, Cowork, Claude Enterprise - one vendor-neutral control across every tool your team uses. It scans in milliseconds.
Real-time guard
Wired as a pre-execution hook in Claude Code, Gemini CLI, Antigravity, Codex CLI, Cursor, GitHub Copilot, Kimi Code CLI, Grok Build, Cline, it refuses a malicious tool call - a hardcoded credential, a typosquatted package - before it runs. The same binary, on macOS, Linux, Windows, and in Docker.
You own the response
It tells you what leaked and where, redacted. What happens next is your team's decision.
Mapped to the standards you track
Every finding is crosswalked against MITRE ATLAS, the OWASP Top 10 for LLM Applications 2025, and CWE, emitted as SARIF 2.1.0 taxonomies your SIEM, ASPM, and GitHub code scanning already speak. See the standards crosswalk.
From a free scanner to fleet-wide coverage.
One binary for every tier, and every tier runs on your own machines. Each paid tier includes the one before it.
Free
The full local scanner
- Every detection rule and attack-chain correlation
- Session search and recall
- The localhost web UI
- Text, JSON, SARIF, and NDJSON output, detected secrets always masked
- CI gating
Register the free license at getskarn.com/free. skarn assess scans with no license at all.
Pro
The paid controls, for one developer
- Policy-as-code
- Baselines with per-entry provenance
- A tamper-evident audit log
- Evidence packs
- Guard enforcement
Team
Pro for 2 to 24 developers, as one organization
- Seats you assign and reclaim
- Invitations
- A verified company domain that developers join themselves
Enterprise
Fleet-scale reporting
- The enterprise reporting profile
- A self-hosted fleet console over redacted findings and metadata (roadmap)
- SSO, RBAC, and audit (roadmap)
Questions, answered.
How do I audit AI coding-assistant sessions for leaked credentials?
Run Skarn on the developer's machine. It reads the on-disk session logs that Claude Code, Gemini CLI, Antigravity, Codex CLI, Cursor, GitHub Copilot, Kimi Code CLI, Grok Build, Grok Bot, OpenCode, Cline, Cowork, and Claude Enterprise already write, finds the leaked credentials and the attacks around them with 251 built-in rules, and produces a redacted, risk-scored report - locally, with no network call by default.
Can Skarn scan my Claude Code, Cursor, or Grok Bot history for secrets?
Yes. Skarn scans the local Claude Code, Gemini CLI, Antigravity, Codex CLI, Cursor, GitHub Copilot, Kimi Code CLI, Grok Build, Grok Bot, OpenCode, Cline, Cowork, and Claude Enterprise session history for leaked API keys, tokens, and .env contents, shows each secret redacted, and uploads nothing.
How is Skarn different from a secret scanner?
A secret scanner finds a key in a repository. Skarn reads the AI session itself, so it finds the key an engineer pasted into a chat and never committed, and it shows what the assistant did with that key. It links the credential read, the prompt injection, and the exfiltration into one scored attack chain. It also vets the assistant's own configuration (hooks, MCP servers, permissions), checks each tool call before it runs, and makes every past session searchable across every assistant.
What about the endpoint agents from cloud secret-scanning platforms?
Some cloud platforms now ship endpoint agents that scan AI session files for credentials. They are built around the vendor's dashboard: an account and workspace to enroll in, finding metadata sent upstream, and a credential inventory as the output. Skarn scans locally with no vendor dashboard, works fully offline, fails closed on a scan it cannot complete, and reads the whole session, so the output covers what happened: the attack chain, the risk score, and the audit-ready report.
Does any data leave the machine?
No. The scan runs entirely on the local machine - no upload, no telemetry, and no network call by default, so the session logs never leave the laptop. `skarn assess` needs no account; `skarn check` needs a free license, and it is verified offline, so nothing leaves the machine even then. The only optional egress is the maintained-feed fetch of signed rule updates on a paid license; no secret ever leaves the machine.
Which AI assistants does it cover?
13: Claude Code, Gemini CLI, Antigravity, Codex CLI, Cursor, GitHub Copilot, Kimi Code CLI, Grok Build, Grok Bot, OpenCode, Cline, Cowork, and Claude Enterprise - one vendor-neutral control across every tool your team uses, from a single binary.
Who is Skarn for?
Security leads and engineering managers in regulated, audit-heavy, or EU data-residency environments who need to see what their developers have leaked into AI tools - without sending anything to a vendor.
Is it open source? What does it cost?
Skarn is closed source, with a free tier that includes the full local product under a license anyone can register for, an individual or an organization alike. Paid tiers add the rest: Pro adds policy-as-code, baselines with per-entry provenance, audit evidence, and real-time enforcement for one developer; Team adds seats and an organization; Enterprise adds fleet-scale reporting, with a self-hosted fleet console on the roadmap. Contact hello@getskarn.com.
Read the evidence
A labeled corpus of AI coding sessions across five assistants, counted incident by incident: which credentials leak, how, and how many were live.
The false-positive rate of the 251 detection rules over the labeled corpus, with the method published so you can rerun it.
How often the prompt-injection-to-exfiltration correlation fires on a session that carries no attack.
Where each assistant writes its session history on disk, and the commands that read it.
The category, what it reads that a git secret scanner does not, and how it differs from DLP and endpoint tools.
The paste-into-assistant channel that no DLP watches, and how to get a measure of it without a proxy.
From the blog
Run skarn assess --cli grokbot against xAI's desktop agent store - local, redacted, no upload.
Run skarn vet over your MCP and hook configuration before a token in a config file becomes a token in a transcript.
See your own exposure in one command.
skarn assess scans every AI coding session on the machine and prints a redacted risk summary. It needs no account and no license, and the scan makes no network call.
The 30-minute live demo runs the scanner with you on a developer's machine; you keep the redacted report. Skarn runs on macOS, Windows, and Linux, on both Intel and ARM.